Gre configuration, Gre overview, Introduction to gre – H3C Technologies H3C SecPath F1000-E User Manual
Page 2: Encapsulation process
1
GRE Configuration
This chapter includes these sections:
•
•
Configuring a GRE over IPv4 Tunnel
•
Configuring a GRE over IPv6 Tunnel
•
Displaying and Maintaining GRE
•
GRE over IPv4 Tunnel Configuration Example
•
GRE over IPv6 Tunnel Configuration Example
•
GRE Overview
Introduction to GRE
Generic Routing Encapsulation (GRE) is a protocol designed for encapsulating and carrying the packets
of one network layer protocol (for example, IP) over another network layer protocol (for example, IP).
GRE is a tunneling technology and serves as a Layer 3 tunneling protocol.
A GER tunnel is a virtual point-to-point (P2P) connection for transferring encapsulated packets. Packets
are encapsulated at one end of the tunnel and de-encapsulated at the other end.
depicts the
encapsulation and de-encapsulation processes.
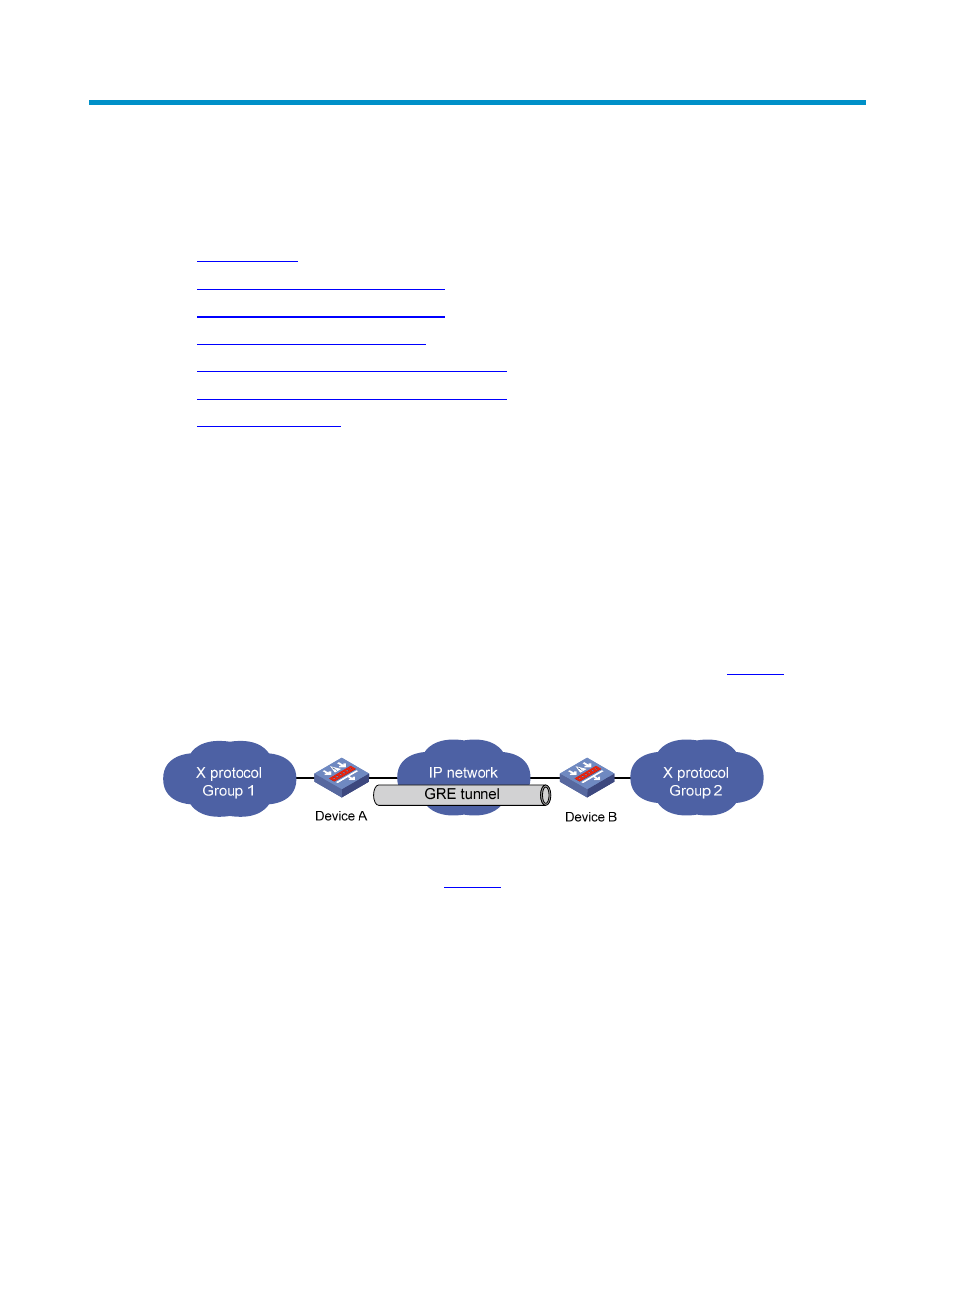
Figure 1 X protocol networks interconnected through the GRE tunnel
The following takes the network shown in
as an example to describe how an X protocol packet
traverses the IP network through a GRE tunnel.
Encapsulation process
1.
After receiving an X protocol packet through the interface connected to Group 1, Device A submits
it to the X protocol for processing.
2.
The X protocol checks the destination address field in the packet header to determine how to route
the packet.
3.
If the packet must be tunneled to reach its destination, Device A sends it to the tunnel interface.
4.
Upon receipt of the packet, the tunnel interface encapsulates it in a GRE packet. Then, the system
encapsulates the packet in an IP packet and forwards the IP packet based on its destination
address and the routing table.