Configuration procedure – H3C Technologies H3C SecPath F1000-E User Manual
Page 28
27
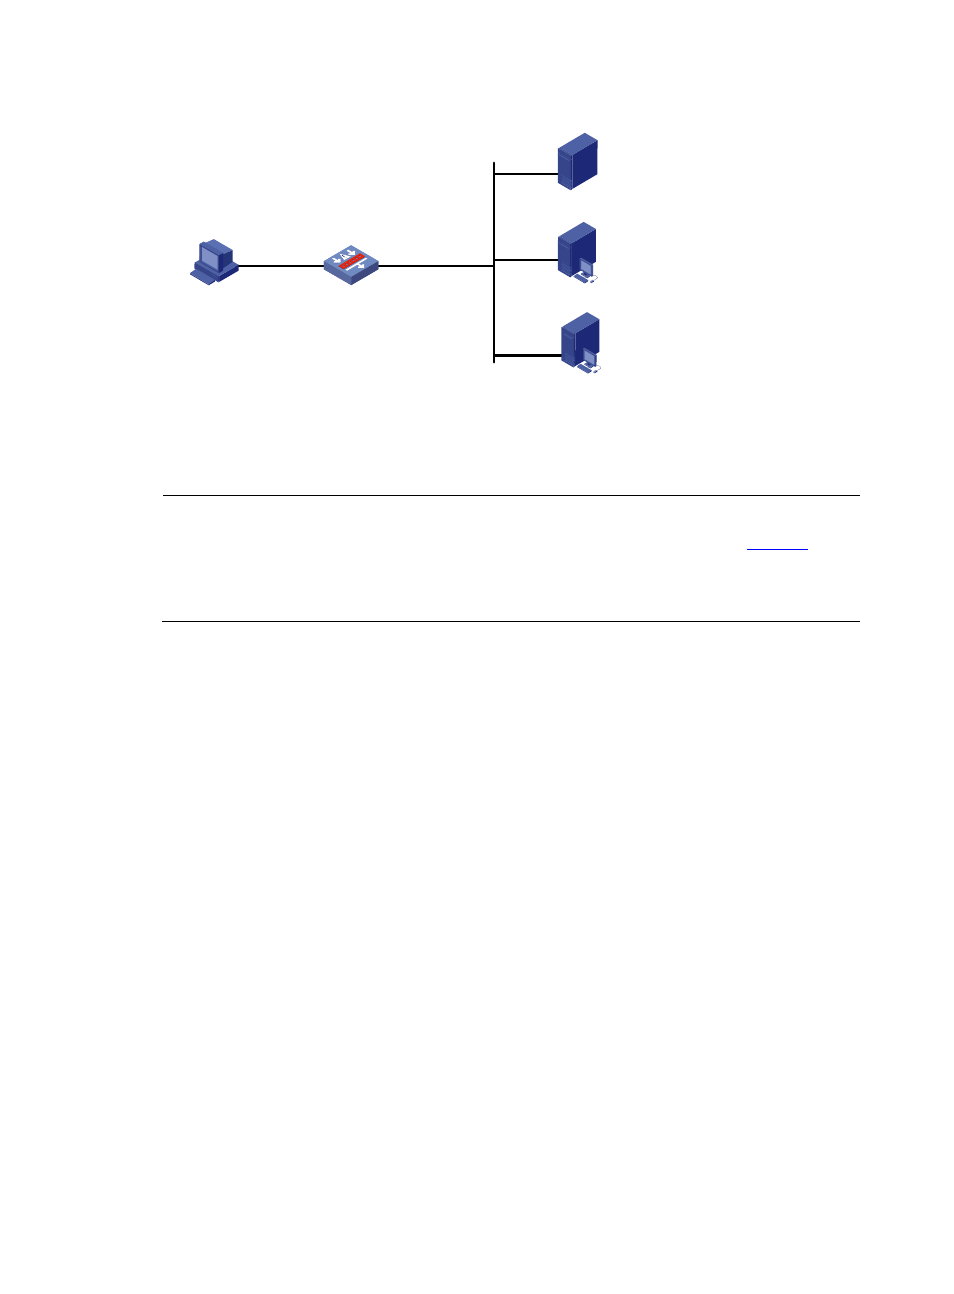
Figure 12 Configure direct portal authentication with extended functions
Device
Host
2.2.2.2/24
Gateway : 2.2.2.1/24
GE0/2
2.2.2.1/24
GE0/1
192.168.0.100/24
Portal server
192.168.0.111/24
RADIUS server
192.168.0.112/24
192.168.0.113/24
Security policy server
Configuration procedure
NOTE:
•
You need to configure IP addresses for the host, Device, and the servers as shown in
and
ensure that they can reach each other.
•
Perform configurations on the RADIUS server to ensure that the user authentication and accounting
functions can work normally.
Perform the following configuration on Device:
Step1
Configure a RADIUS scheme
# Create a RADIUS scheme named rs1 and enter its view.
<Device> system-view
[Device] radius scheme rs1
# Set the server type for the RADIUS scheme. When using the CAMS or iMC server, you need set the
server type to extended.
[Device-radius-rs1] server-type extended
# Specify the primary authentication server and primary accounting server, and configure the keys for
communication with the servers.
[Device-radius-rs1] primary authentication 192.168.0.112
[Device-radius-rs1] primary accounting 192.168.0.112
[Device-radius-rs1] key accounting radius
[Device-radius-rs1] key authentication radius
[Device-radius-rs1] user-name-format without-domain
# Configure the IP address of the security policy server.
[Device-radius-rs1] security-policy-server 192.168.0.113
[Device-radius-rs1] quit
Step2
Configure an authentication domain
# Create an ISP domain named dm1 and enter its view.
[Device] domain dm1