H3C Technologies H3C SecPath F1000-E User Manual
Page 32
Advertising
24
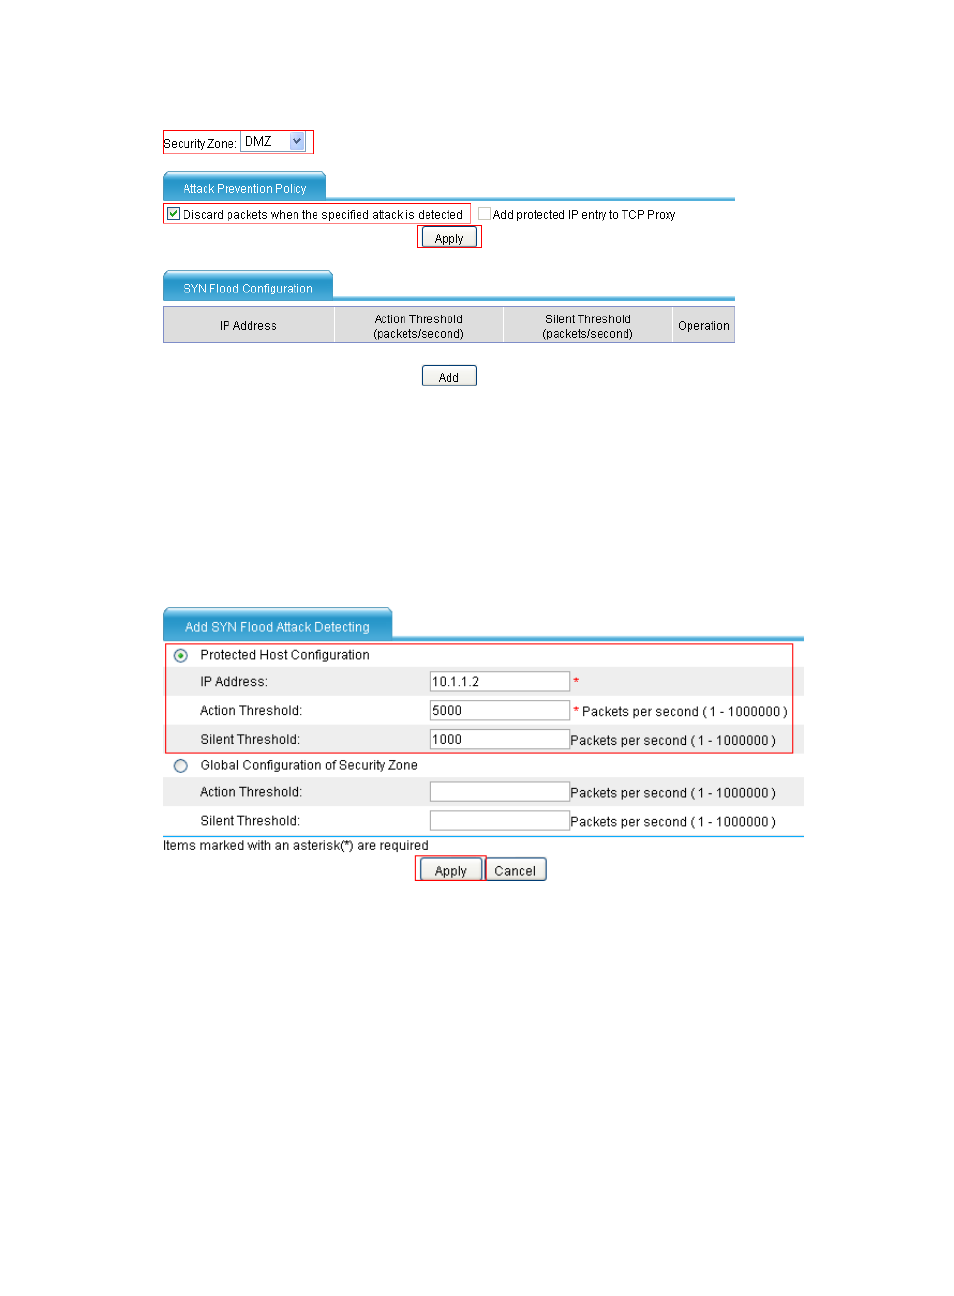
Figure 26 Configuring SYN flood detection for the DMZ
Perform the following operations on the page:
•
Select zone DMZ.
•
In the Attack Prevention Policy area, select the Discard packets when the specified attack is
detected option.
•
Click Apply.
•
In the SYN Flood Configuration area, click Add. The SYN flood attack detection page appears.
Figure 27 Configuring a SYN flood attack detection rule for the server
Perform the following operations on the page:
•
Select the Protected Host Configuration option.
•
Specify the IP address as 10.1.1.2.
•
Set the action threshold to 5000 packets per second.
•
Set the silent threshold to 1000 packets per second.
•
Click Apply to complete the configuration.
Advertising
This manual is related to the following products:
- H3C SecPath F5000-A5 Firewall H3C SecPath F1000-A-EI H3C SecPath F1000-E-SI H3C SecPath F1000-S-AI H3C SecPath F5000-S Firewall H3C SecPath F5000-C Firewall H3C SecPath F100-C-SI H3C SecPath F1000-C-SI H3C SecPath F100-A-SI H3C SecBlade FW Cards H3C SecBlade FW Enhanced Cards H3C SecPath U200-A U200-M U200-S H3C SecPath U200-CA U200-CM U200-CS