8 access control, 1 layer3 based acl – PLANET WGSD-1022 User Manual
Page 78
4.8 Access Control
An ACL consists of a set of rules which are matched sequentially against a packet. When a packet meets
the match criteria of a rule, the specified rule action (Permit/Deny) is taken and the additional rules are
not checked for a match. On this menu the interfaces to which an ACL applies must be specified, as well
as whether it applies to inbound or outbound traffic. Rules for the ACL are specified/created using the
ACL Rule Configuration menu.
4.8.1 Layer3 Based ACL
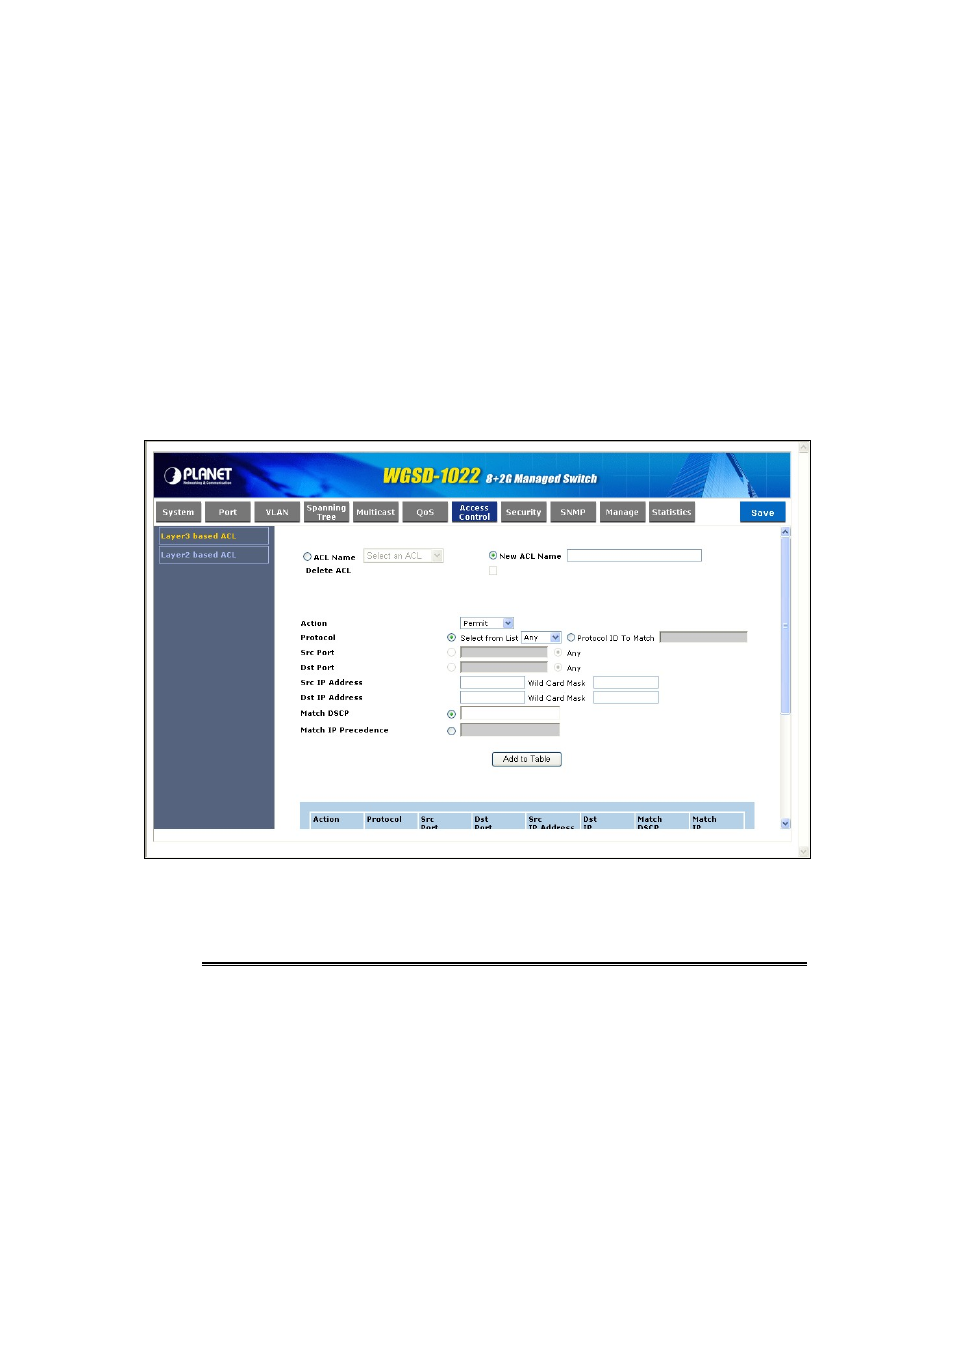
The layer3 Based ACL (Access Control List) screen (see figure 4-37) contains information for defining IP
Based ACLs.
Figure 4-37 Layer3-Base ACL screen
The Page contains the following fields:
• ACL Name
Displays the user-defined IP based ACLs
• New ACL Name
Defines a new user-defined IP based ACL
• Delete ACL
By which deletes the selected ACL
• Action
Indicates the action assigned to the packet matching the ACL.
Packets are forwarded or dropped. In addition, the port can be
shutdown, a trap can be sent to the network administrator, or a packet
assigned rate limiting restrictions for forwarding. The options are as