H3C Technologies H3C SecPath F1000-E User Manual
Page 607
15
•
Select Permit as the operation.
•
Select the Source IP Address check box, and type 10.1.1.12 and 0.0.0.0 in the following text
boxes.
•
Click Apply.
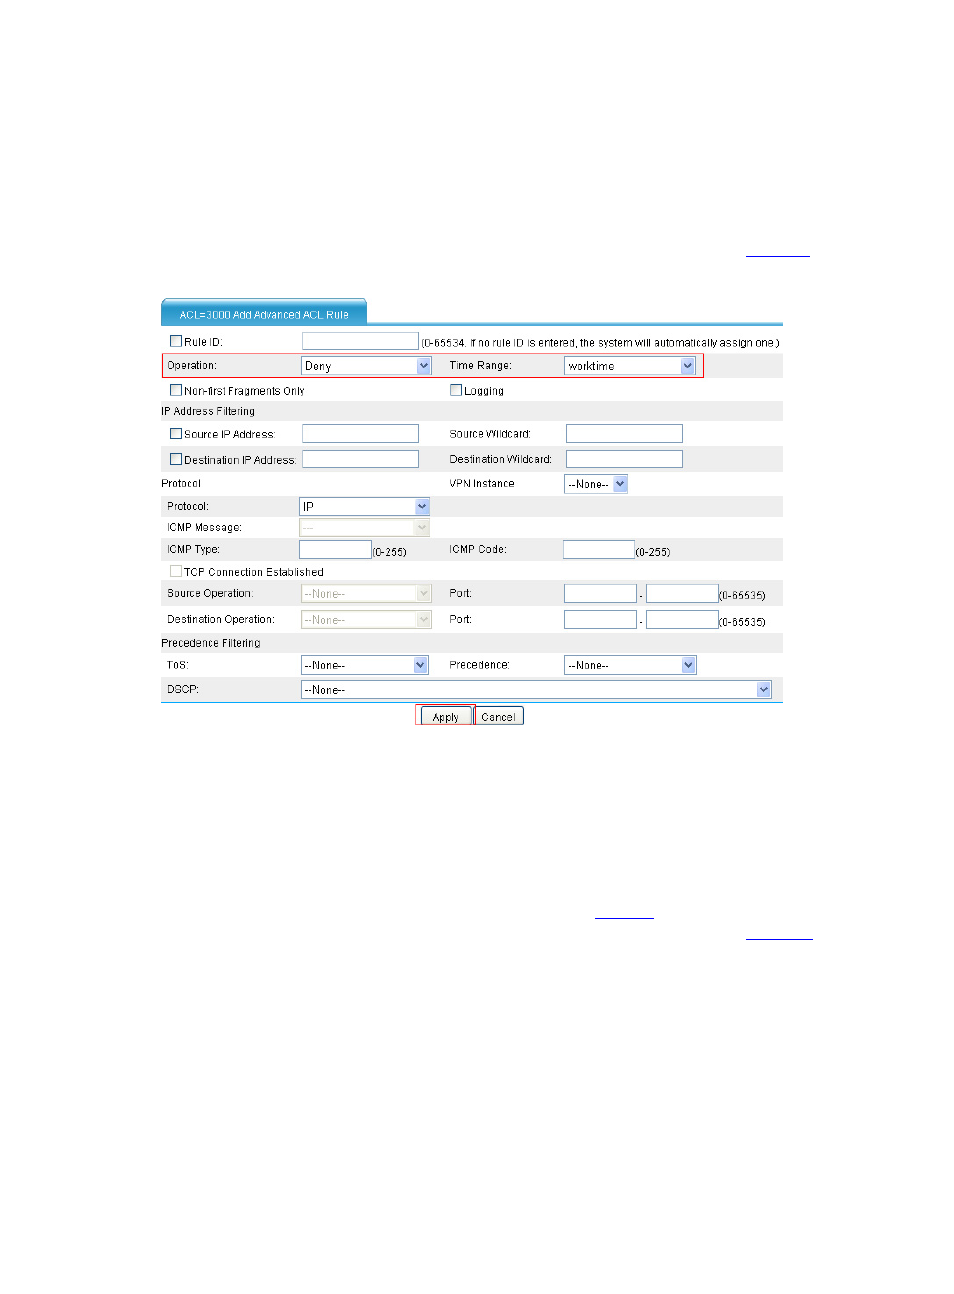
# Configure a rule to deny access of all the other hosts to the external network during working time.
•
On the page that lists the rules, click Add. Perform the configurations shown in
.
Figure 19 Deny all the other hosts' access to the external network during working time
•
Select Deny as the operation.
•
Select the time range worktime.
•
Click Apply.
# Configure the interzone policy group.
•
Select Firewall > Security Policy > Interzone Policy Group from the navigation tree to
enter the interzone policy group list page, as shown in
. Then click Add to enter the
interzone policy group configuration page. Perform the configurations shown in
.