H3C Technologies H3C SecPath F1000-E User Manual
Page 802
28
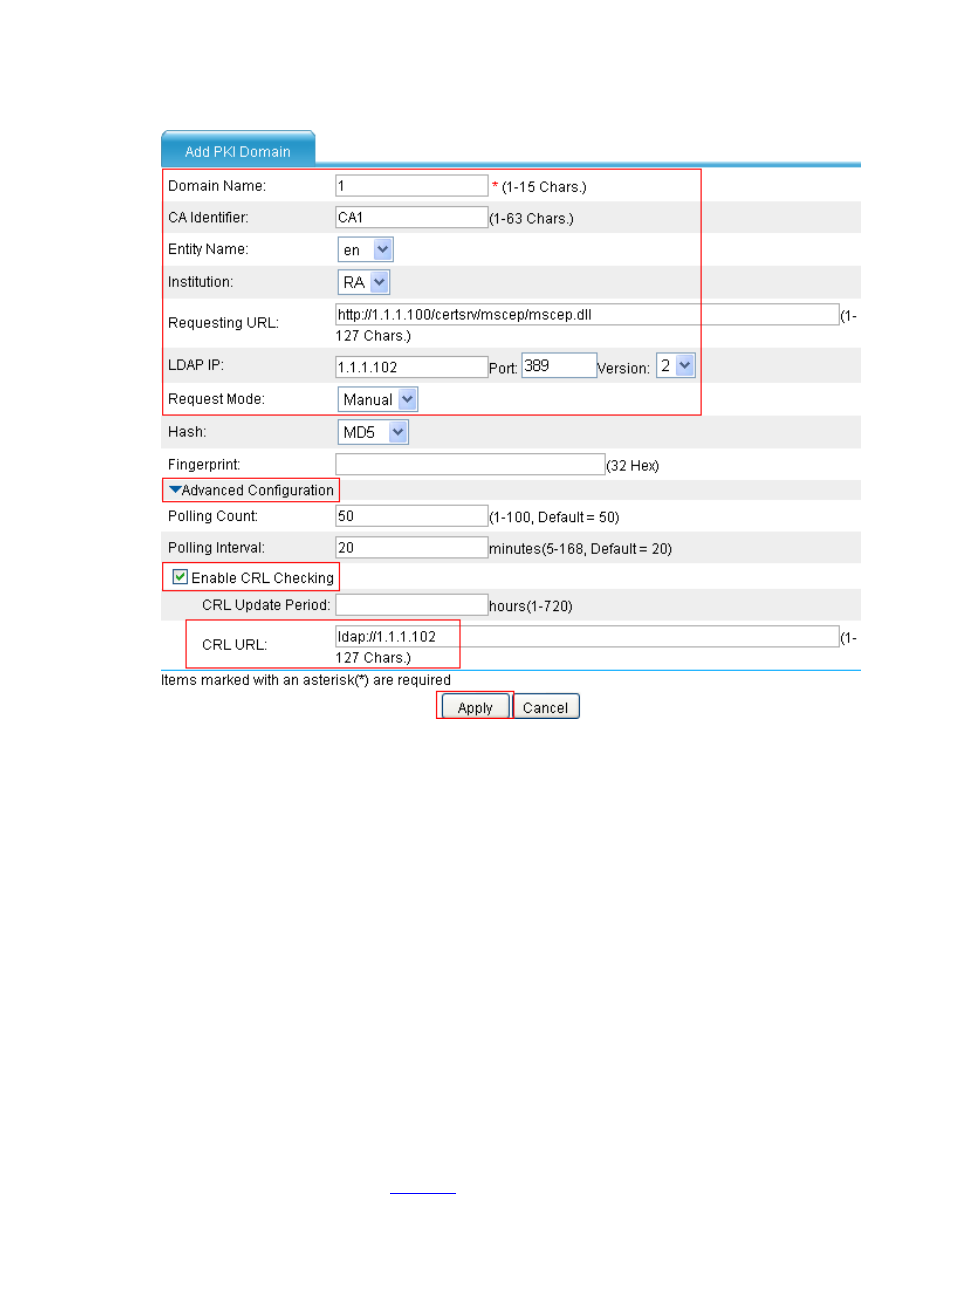
Figure 31 Add PKI domain
•
Type 1 as the PKI domain name.
•
Type CA1 as the CA identifier.
•
Select en as the local entity.
•
Select RA as the authority for certificate request.
•
Type http://1.1.1.100/certsrv/mscep/mscep.dll as the URL for certificate request. (The RA
URL given here is just an example. Configure the RA URL as required.)
•
Type 1.1.1.102 as the IP address of the LDAP server, 389 as the port number, and select 2 as the
version number.
•
Select Manual as the certificate request mode.
•
Click the expansion button before Advanced Configuration to display the advanced
configuration items.
•
Select the Enable CRL Checking check box.
•
Type ldap://1.1.1.102 as the URL for CRLs.
•
Click Apply. When the system displays “Fingerprint of the root certificate not specified. No root
certificate validation will occur. Continue?”, click OK to confirm.
# Generate an RSA key pair.
•
Select VPN > PKI > Certificate from the navigation tree and then click Create Key to perform
the configurations shown in
.